


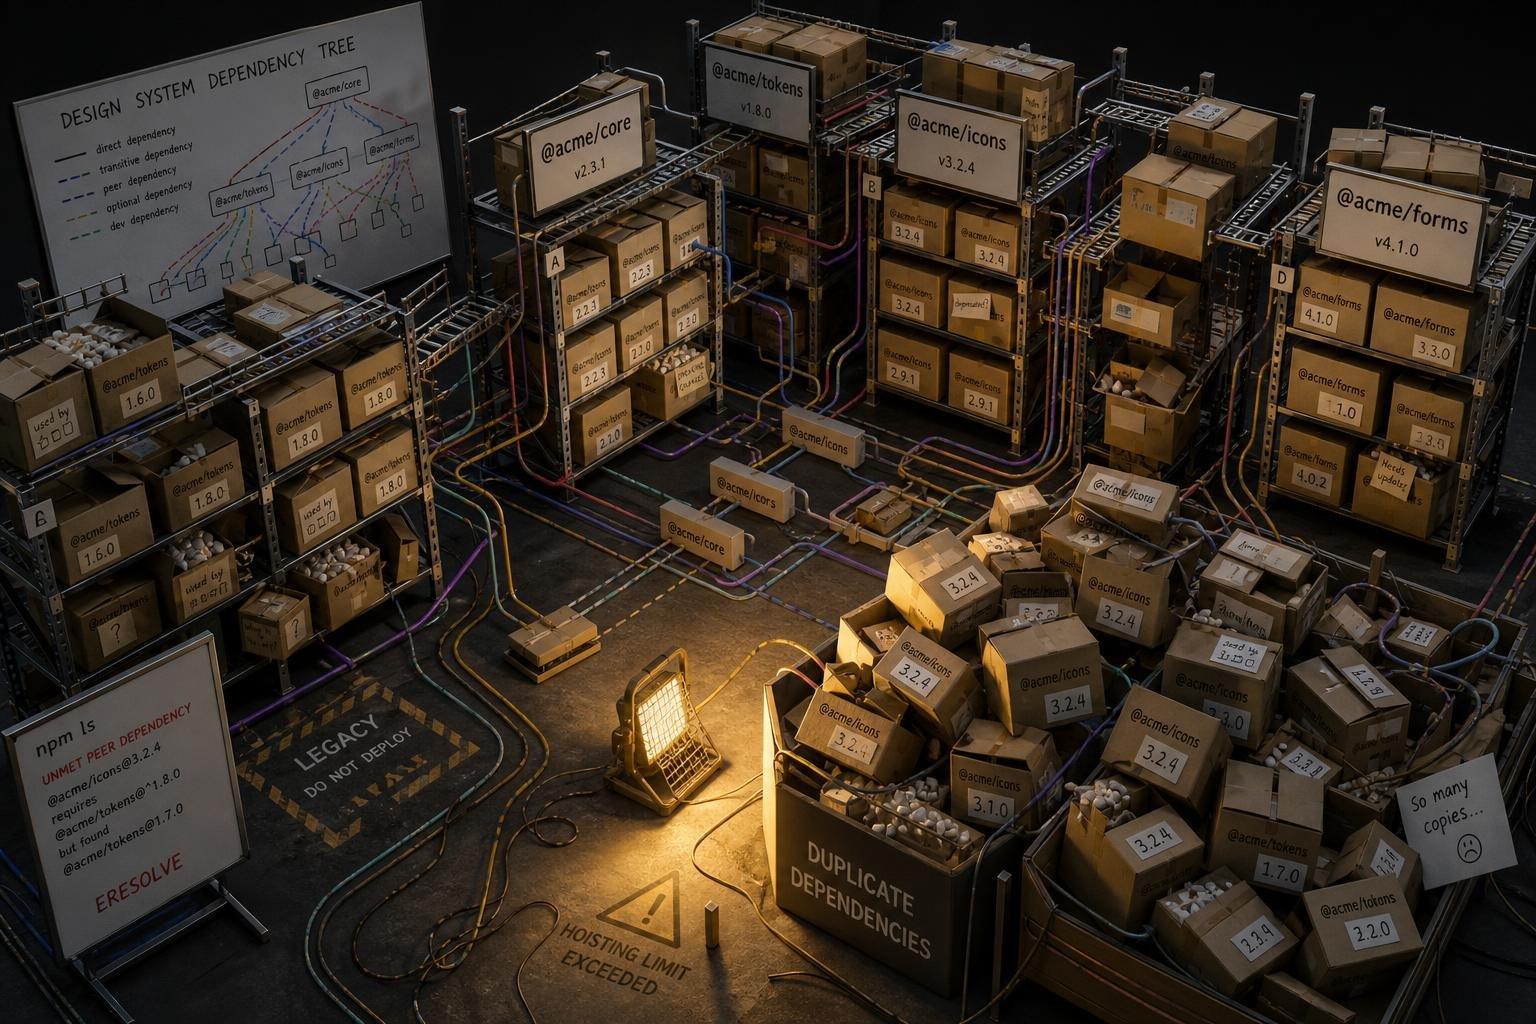

A design system team I talk to regularly hit the same wall last year that a backend team hit with microservices: they looked at their one growing package and decided the fix was more repositories, more package.json files, more independent release cadences. It felt like architecture. It was mostly busywork wearing architecture's clothes.
The instinct is understandable. One @acme/ui package with buttons, tokens, icons, and form primitives all bundled together starts to feel like a junk drawer. Splitting it into @acme/tokens, @acme/icons, @acme/forms, and @acme/core looks like discipline. But the backend version of this story has already been run, and it ended badly enough that it's worth borrowing the lesson before your design system repeats it.
The Modular-Monolith Lesson, Applied to Components
A backend engineer who split a Django monolith into five microservices — Users, Billing, Notifications, Orders, Reporting — before his team actually needed the separation wrote candidly about what it cost: a two-day feature became a one-week feature because changes now touched three repos and three deployments in sequence, transactional guarantees that transaction.atomic() gave for free had to be rebuilt by hand with retries and idempotency keys, and debugging a missing email meant tracing a request across a gateway, two services, and a queue instead of just reading one log (The Backend Tech Lead). None of the reasons for splitting were wrong — the monolith genuinely was getting messy, scaling genuinely was coming. The problem was solving a future problem with present-day complexity.
Design systems fail the same test. Splitting tokens from components from icons into separate npm packages buys you independent versioning you don't need yet, at the cost of cross-package PRs, coordinated releases, and a consumer who now has to understand which combination of four package versions actually works together. If your "junk drawer" problem is really a naming and folder-structure problem inside one package, more packages won't solve it — they'll just relocate the mess into a monorepo's workspace config.
What a Real Monorepo Migration Actually Costs You
The honest version of this tradeoff shows up in the tooling, not the architecture diagram. One maintainer who moved a design-system monorepo off Lerna and onto a lighter publish tool described a migration where the package code barely changed but the lockfile did — thousands of lines rewritten — because the old setup didn't understand pnpm's workspace: protocol, so internal packages were pinned to fixed versions and a package from the team's own repo was getting re-downloaded from npm (DEV Community). Two years after that fix, a new kind of debt showed up: seven packages all repeating the same dependency versions, solved by consolidating everything into a single pnpm catalog file. The lesson he landed on — measure a tool by what it costs the next person who has to understand it without you — is the right filter for a split-packages decision too. Before you cut @acme/ui into five packages, ask who inherits the job of keeping five package.json files, five changelogs, and five release pipelines in sync a year from now.
That same filter applies outside the monorepo-vs-multirepo question. A founder writing about when React Native projects actually need a monorepo put it bluntly: count your apps first, because "the most expensive thing you can do in week one is restructure a repository to solve a problem the framework already solved" (Newly). Swap "framework" for "single well-organized package" and the advice holds for design systems just as well.
One Package, Multiple Release Channels, No Package Explosion
Shopify's Polaris offers a useful counter-model. Rather than splitting into separate npm modules per concern, Polaris ships its web components through versioned CDN channels under one semver model — polaris.js, polaris-1.js, and now polaris-2.js for the 2.0 stable release that matches the redesigned Shopify admin (Shopify). Consumers choose which major version to pin to, but the system itself stays one coherent thing to maintain, not a federation of packages that each need their own breaking-change story.
The pattern worth watching for in your own system isn't "monorepo good, multirepo bad." It's whether a split is answering an ownership problem you actually have — separate teams, genuinely independent release cadences, consumers who need only a slice — or whether it's a reorganization dressed up as a fix for a codebase that just needs better internal structure. If you can't name the team that owns the seam between two proposed packages, you don't have two packages yet. You have one package with a folder you haven't cleaned up.